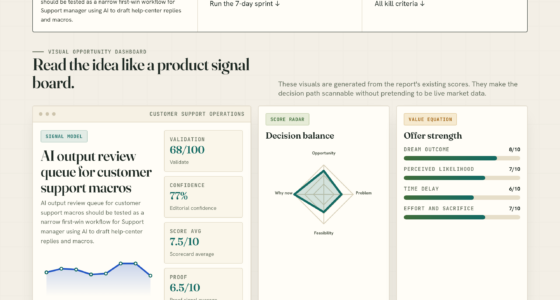
📊 Full opportunity report: Device Security For Remote Teams: Avoiding Hardware Security Gaps on IdeaNavigator AI — validation score, market gap, and execution plan.

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
A new device security checker for remote teams has been introduced, targeting SMBs with mixed hardware. It verifies encryption, updates, and screen locks, reporting compliance status without invasive management. This addresses a critical gap in remote device security verification.
A new lightweight device security checker has been developed to help remote teams verify the security posture of employee-owned and mixed-OS devices. The tool, which is currently in initial testing, aims to address a growing compliance gap for SMBs facing SOC 2 and customer security reviews, where traditional management tools are too invasive for personal devices. This development could provide a scalable, non-intrusive way to ensure hardware security standards are met across diverse device fleets.
The device security checker is a voluntary, lightweight agent that employees install on their personal devices, including MacBooks, Windows laptops, and unmanaged phones. It performs checks for disk encryption, OS updates, screen lock activation, and password manager presence. The results are reported to a centralized dashboard, offering a pass/fail status for each device, along with self-remediation instructions—without remote control or invasive management. The initial deployment involves ten remote startups, with plans to measure device enrollment rates and assess whether auditors accept the generated reports as sufficient evidence of security posture.
This approach aims to fill a verification gap created by the limitations of mobile device management (MDM) solutions, which are often considered too intrusive for employee-owned devices. Instead, this tool offers a lightweight, voluntary alternative suited for SMBs that need to demonstrate compliance without overstepping employee privacy or control boundaries. The service will be offered on a per-device monthly pricing model, with additional features such as compliance report exports on paid tiers.
Potential Impact on SMB Remote Security Compliance
This development could significantly improve how small and medium-sized businesses verify the security of their remote workforce’s personal devices. As regulatory and customer demands for security posture evidence increase, especially with SOC 2 and similar standards, having a simple, non-invasive tool to verify device encryption, updates, and security settings becomes critical. By enabling scalable and voluntary device checks, companies can better mitigate hardware security gaps, reduce risk exposure, and meet compliance requirements without deploying heavy-handed MDM solutions that employees may resist. This approach could also influence broader SMB security practices, emphasizing lightweight, employee-friendly verification methods.
device security checker for remote work
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Need for Non-Invasive Device Security Checks in Remote Work
The shift to remote work has led many SMBs to rely on personal devices for work-related activities. These devices often include a mix of outdated hardware and unmanaged phones, creating security vulnerabilities that are difficult to monitor and verify. Traditional endpoint security solutions, such as enterprise-grade mobile device management (MDM), are often considered too invasive for employee-owned devices, leading to resistance and compliance gaps. In response, security teams are seeking lightweight, voluntary tools that can quickly assess device security posture and provide evidence for audits like SOC 2.
Recent market trends indicate an increased focus on SMB endpoint security, driven by rising regulatory scrutiny and the need to demonstrate compliance with security standards. The proposed device checker aims to address this by offering a simple, scalable solution that can be deployed rapidly at small organizations, providing a practical alternative to more invasive management platforms.
Uncertainties About Adoption and Auditor Acceptance
It is still unclear how quickly SMBs will adopt this new device checker and whether security auditors will accept the reports as sufficient evidence of compliance. The initial deployment at ten startups will provide some insights, but broader validation is needed to confirm its effectiveness and acceptance in various regulatory contexts. Additionally, questions remain about long-term user engagement and whether employees will consistently install and run the agent voluntarily.
Next Steps for Deployment and Validation
The initial phase involves deploying the device checker at ten remote startups, measuring enrollment rates, and gathering feedback from security teams and auditors. Success metrics include high device enrollment, positive auditor acceptance, and demonstrable improvements in security posture. Based on these results, the company plans to refine the tool, expand deployment, and explore integration with existing security workflows. Further validation will be necessary to establish the tool as a standard SMB security verification method.
Key Questions
How does the device security checker work?
The agent installed on employee devices performs checks for disk encryption, OS updates, screen lock activation, and password manager presence, then reports the results to a central dashboard.
Is this tool suitable for all types of devices?
Yes, it is designed to work across Mac, Windows, and unmanaged phones, focusing on common security settings relevant to SMBs.
Will employees need to give up control of their devices?
No, the tool is voluntary and does not involve remote control or invasive management; it simply reports security posture for compliance purposes.
When will this tool be generally available?
Deployment is in the early testing phase; broader availability depends on initial results and feedback from participating startups.
Will auditors accept these reports for compliance?
Acceptance is still being evaluated; initial plans include validating the reports with auditors during the pilot phase.
Source: IdeaNavigator AI
Columbus Day / Indigenous Peoples' Day Picks
long weekend sales
As an affiliate, we earn on qualifying purchases.